
The test in NVIDIA’s OpenShell 0.1.0 guide is small: put a program in a sandbox, deny its network request, then change the policy so it can read from GitHub but cannot post to the same API. Developers can inspect the decisions without running a language model or supplying an API key.
Published September 28, 2026, the guide is a practical follow-up to OpenShell’s broader platform story, not a new model release. NVIDIA says the runtime can place controls around existing agents, including Codex and Claude Code, without rewriting them. The walkthrough uses curl to demonstrate the policy boundary; NVIDIA says the same controls apply when an agent makes the request. The demo has not been independently reproduced here.
An instruction telling an agent to “only read GitHub” depends on the agent following it. OpenShell puts the restriction outside the agent’s workload and checks what its programs try to do.
Start With a Sandbox That Cannot Reach the Network
NVIDIA’s example begins after installing OpenShell 0.1.0 and downloading the guide’s no-network.yaml and github-readonly.yaml files into an examples directory. The first command creates a sandbox named policy-demo using the no-network policy:
openshell sandbox create --name policy-demo \
  --no-auto-providers \
  --policy examples/no-network.yaml
According to the guide, the command opens a shell inside the sandbox. A request to GitHub’s public /zen endpoint should then fail:
curl -sS --max-time 10 https://api.github.com/zen
The endpoint requires no GitHub credential, keeping the test focused on network permission. The request is blocked before authentication could complicate the result. From a second terminal on the host, the operator can inspect the recorded decision:
openshell logs policy-demo --since 5m
The initial failure establishes what the sandbox cannot do before access is granted. If a developer began with unrestricted networking, a successful GitHub request would say little about whether the intended rule was working.
The separate host terminal lets an operator check whether OpenShell denied the request and which program made it. An agent may report that a command failed, but a network error alone would not identify the cause.
Permit GitHub Reads, Then Test a Write
The replacement policy targets a specific program and destination. This is the rule NVIDIA shows in its github-readonly.yaml example:
network_policies:
  github_api:
    name: github-api-readonly
    endpoints:
      - host: api.github.com
        port: 443
        protocol: rest
    enforcement: enforce
    access: read-only
    binaries:
      - path: /usr/bin/curl
The rule names /usr/bin/curl, specifies the GitHub API host and port, and uses protocol: rest so OpenShell can inspect the HTTP request. NVIDIA says the read-only setting allows the demonstrated read while blocking a write request.
From the host terminal, the operator applies the complete replacement policy to the running sandbox:
openshell policy set policy-demo \
  --policy examples/github-readonly.yaml --wait
NVIDIA’s sequence does not restart the sandbox. Back inside its shell, the guide compares a normal request with an explicit POST:
curl -sS --max-time 10 https://api.github.com/zen
curl -sS --max-time 10 -X POST https://api.github.com/zen
NVIDIA says the first request succeeds and OpenShell blocks the second. The operator checks openshell logs policy-demo --since 5m again to confirm the POST was denied by policy. A failed POST alone would not prove the sandbox stopped it, because the remote API might also reject the request.
The example demonstrates a rule for curl against one API host. It does not grant universal GitHub permission to every executable an agent might launch. Teams adapting it for a coding agent need to account for the programs that agent actually runs and the services its task requires.
The Request Check Happens Outside the Agent
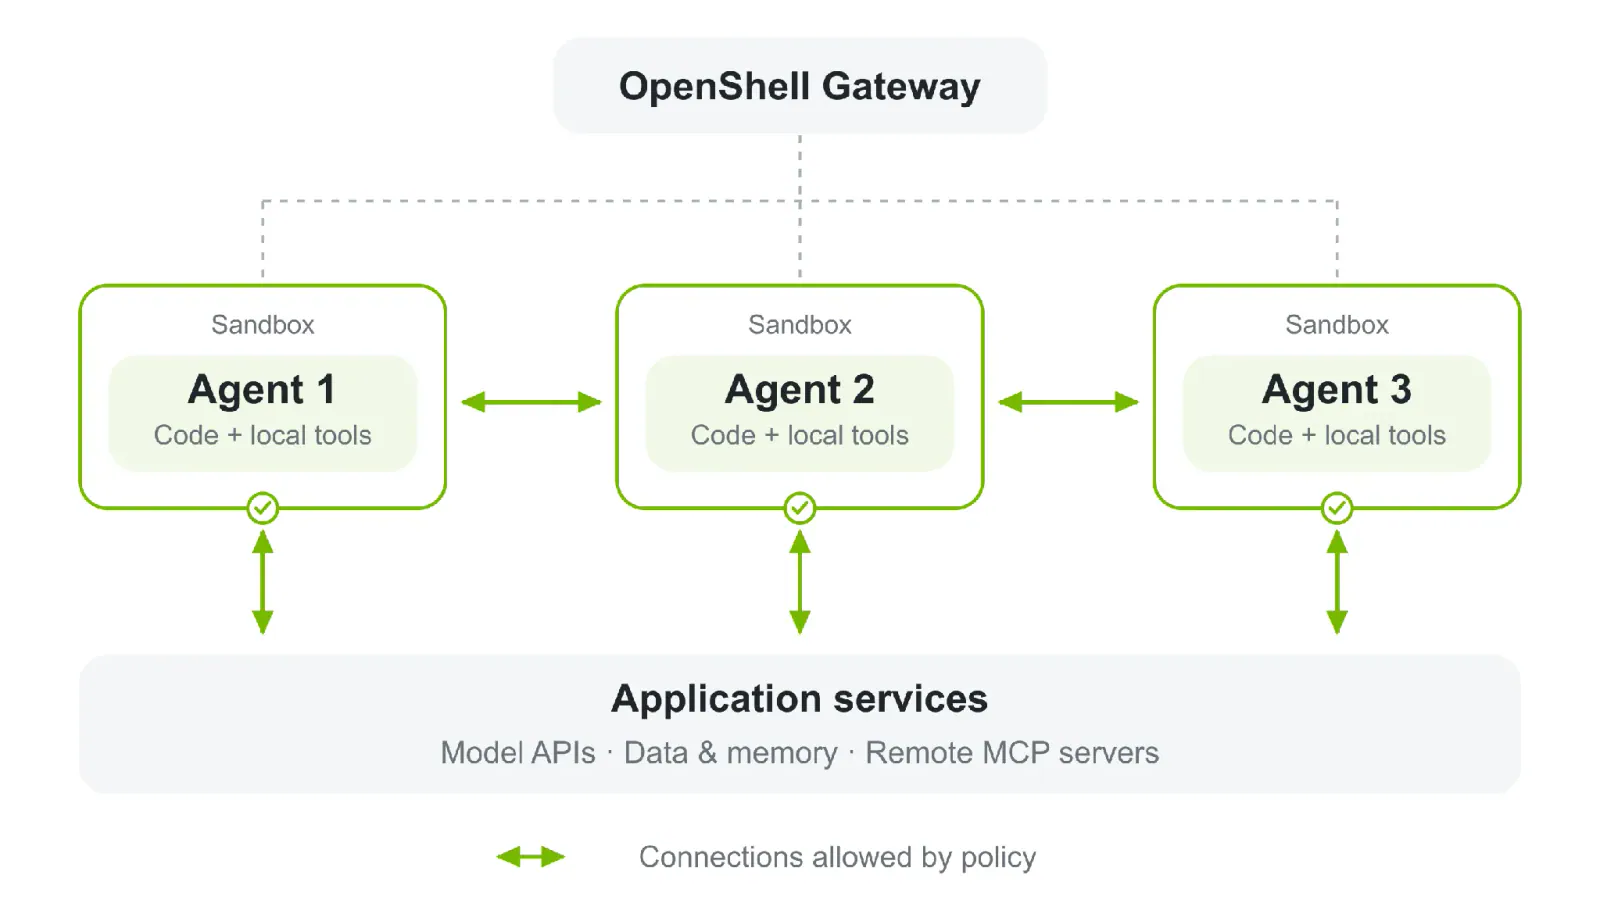
NVIDIA describes three parts of the runtime on its OpenShell architecture page. The gateway manages sandbox lifecycles and policies. A supervisor paired with each sandbox checks outbound requests against policy while running outside the agent workload. The sandbox applies kernel-level controls to the workload’s files and processes and, according to NVIDIA, has no network path except through its supervisor.
A coding agent can open a shell, run generated code, or start a child process. Rules expressed only in the agent’s prompt may not constrain what those programs attempt. NVIDIA says OpenShell’s runtime controls continue to apply to those actions because enforcement is external to the workload.
For configured traffic, the supervisor can inspect more than a destination address. NVIDIA says it can evaluate HTTP, GraphQL, and Model Context Protocol requests, permitting a query while blocking a write through the same service. Policies are authored in YAML and compiled to OPA/Rego for evaluation. OpenShell also records policy decisions in an audit trail, giving operators evidence of what was allowed or denied.
Those are NVIDIA’s descriptions of the system, not results from an independent security assessment. The GitHub exercise shows developers how to inspect one policy decision; it does not establish that every possible agent behavior has been tested.
Keep Service Credentials Out of the Workload
The public GitHub test needs no secret. Real agents often need model APIs or private services. Can an agent use one of those services without receiving its reusable credential?
NVIDIA says OpenShell keeps the real credential outside the agent workload and substitutes it only for an authorized request to an approved endpoint. A provider profile defines the service credentials, endpoints, and permitted programs. Both network policy and credential binding must allow a request; granting access to one destination does not make its credential available to another.
Frequently Asked Questions
4 questions
1Can OpenShell Run Codex or Claude Code Without Rewriting Them?
NVIDIA says OpenShell can place runtime controls around existing agents, including Codex and Claude Code, without changes to their agent code. Its guide includes a Codex launch command that attaches an already configured GitHub provider. The specific no-network and read-only GitHub tests use curl, however, rather than a demonstrated run of either coding agent.
2
Sources
- OpenShell 0.1.0 guidedeveloper.nvidia.com
- OpenShell architecture pagenvidia.com




